astronaut
 Pearl
 Hyperliquid
 Walrus
 Pudgy Penguins
 Bitcoin
 NEAR Protocol
Key Insights:
- Lazarus Group stole Solana, bridged funds to Ethereum, and used Tornado.
- Investigators flagged $1.6M laundered via Tornado Cash addresses.
- Over $1.25M remains dormant in an Ethereum wallet, likely awaiting laundering.
On May 16, 2025, crypto security researchers detected some complex cyberattacks that led to the hacking of 3.2 million Solana (SOL) tokens. Blockchain forensics has identified the exploit as the work of the North Korean-affiliated Lazarus Group.
The assault was initially marked by an on-chain observer, ZachXBT, who identified unusual transfers on a Solana account identified as C4WYtB…e525. They emptied several Solana wallets, quickly swapped them, and bridged into Ethereum, which is an example of a repeat laundering strategy that Lazarus-linked hacks have adopted.
Cross-Chain Laundering: From Solana to Ethereum
The record of the transactions on the blockchain suggests that the stolen money was transferred through the bridging infrastructure. This enabled the hackers to avoid direct traceability. After this action, the money was transferred into Ethereum (ETH), currently struggling to reach its bottom, and scattered on numerous wallets, hiding its track.
Data shows various Solana-compatible wallet outflows moving to the C4WYtB…e525 wallet. Then, the tokens were deposited into Ethereum and divided into different Ethereum accounts, such as 0xd5de…5b13, 0x7cfa7…00df, and 0xa5f9…d528, which were related to the same $3.2 million exploit.
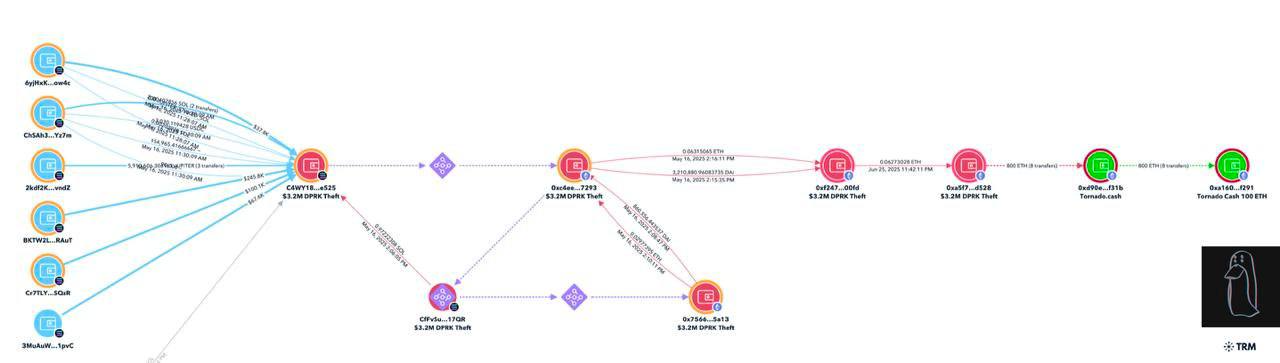
On June 25 and June 27, 800 ETH, or about $1.6 million, of the laundered ETH was transferred to Tornado Cash during two transactions. Tornado Cash is an Ethereum mixer that a crypto user can utilize to conceal transaction history and frequently wash the stolen funds by cybercriminals.
Tornado Cash Once Again in the Spotlight
The involvement of the attacker with Tornado Cash reflects some previous Lazarus activities since laundering routes were based on token exchanges, decentralized exchanges, and mixers that do not conduct Know Your Customer (KYC) checks. Tornado Cash can still operate via the use of decentralized hosting and open-source infrastructure, in spite of being sanctioned by the U.S. Treasury in 2022.
Addresses of 0x9c09…f31b and 0xa41d0…f291 were employed in order to launder the 800 ETH via Tornado Cash, a process that essentially broke and anonymized the breadcrumb. The money was split into chunks of 100 ETH, which is a well-recognized mechanism of concealing the fragments of transactions displayed by blockchain surveillance platforms.
There is one wallet, 0xa5f9…d528. Its total balance, including ETH and DAI, is approximately $1.25 million, which indicates that some of the stolen funds have yet to be laundered. Analysts conclude that such funds can be lying idle or are waiting to be subjected to more retarding tactics.
As the transaction graph recounts, the transaction originated with at least seven Solana wallets transferring funds to a centralized pooling wallet, C4WYtB…e525. A bridge transaction was then instant-moving out of this wallet, which converted the Solana tokens to Ethereum-compatible tokens and disseminated them to the three crucial addresses of ETH.
Every stage in the laundering process, such as 0xd5de…5b13 to 0x7cfa7…00df to 0xa5f9…d528, had the DPRK Theft tag of TRM, confirming this activity was linked to the Lazarus Group. This money was then advanced into Tornado Cash to be anonymized in the last stages of the laundering process.
Lazarus Group Adds NFT Exploits to Toolkit
Since its emergence in 2017, the Lazarus Group has perfected its methods of stealing and laundering cryptocurrencies. Later, it can easily avoid direct asset recovery attempts by pairing wallet security vulnerabilities and using cross-chain bridges. Such attacks by Lazarus usually contain phishing, injection, malware, and misuse of the smart contracts, followed by rapid liquidity of assets and cleaning.
The May 16 Solana attack is closely related to other Lazarus-centered attacks, including the 2022 $100 million Horizon Bridge attack and the 2025 early-year Lazarus-centered $1.5 billion Bybit hack. All of them show the adaptive set of tools, including NFT mints, instant exchange, and decentralized applications, such as Tornado Cash.
Other indicators of Lazarus operations in the forensic realm include GitHub and code repositories set up in Korean, VPN usage, and system time zones connected to DPRK infrastructure. These trends strengthen the status of the group defined by the United States government as an Advanced Persistent Threat (APT) acting according to the direct instructions of North Korean intelligence divisions.
In late June, security researchers also found associated exploits of NFT projects ChainSaw and Favrr. Vulnerabilities were exploited to mint unauthorized NFTs, adding another million dollars in losses. All this money was also partially laundered through known centralized exchanges that had high liquidity levels. The new hack is part of the estimated 1.6 billion that North Korea has stolen in digital assets in 2025 alone.
Disclaimer
This article is for informational purposes only and provides no financial, investment, or other advice. The author or any people mentioned in this article are not responsible for any financial loss that may occur from investing in or trading. Please do your research before making any financial decisions.