astronaut
 Pearl
 NEAR Protocol
 Starknet
 Zcash
 Pudgy Penguins
 Ethena

DeFi protocol Makina Finance has lost around $5 million due to a smart contract exploit. Blockchain security firm Certik reported the attack Monday night.
He noted that the funds were drained from one of Makina Finance’s pools. The incident affected Makina’s Dialectic USD DUSD/USDC stableswap pool.
How did the Attack Happen?
According to Certik, the exploit occurs when the attacker uses a flash loan to manipulate the Makina Finance oracle. With a $280 million USDC flash loan, the attacker used $170 million to manipulate the MachineShareOracle. This determines the DUSD/USDC pool pricing.
With this, the hacker was able to swap the remaining $110 million USDC to drain the pool of around 5 million USDC. Certik’s security engineer, nobody, further explained how the attack happened, noting the unique nature of the DUSD pool.
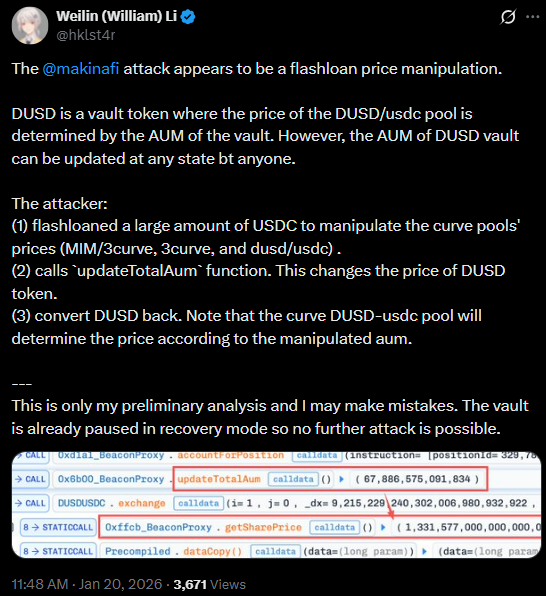
The pool has an ‘updateTotalAum’ function that allows permissionless updates to the price of the DUSD token. That gave the attacker free rein.
They wrote:
Thus, he believed it was a mix of a flash loan and a permissionless AUM update that enabled the exploit. The hacker executed the exploit in a single transaction. They refreshed the price oracle mid-transaction. This action allowed them to complete the attack successfully.
Reports on the amount lost have varied across blockchain security firms. While Certik pegs it around $5 million, Peckshield says it is $4.13 million. GoPlus puts the number at $5.1 million. TenArmor reported that it is around $4.2 million.
Interestingly, the attacker did not take most of the stolen funds with a MEV bot front-running the transaction. The bot with the address 0xa6c2 was about to drain $4.1 million from the pool in a series of trades. It has now moved the stolen funds to two new addresses.
Makina Finance Confirms Exploit, Says It is Isolated
Meanwhile, the DeFi protocol has confirmed the hack, noting it is an isolated incident that does not affect all its pools. The protocol called on liquidity providers for the DUSD Curve pool to remove their liquidity.
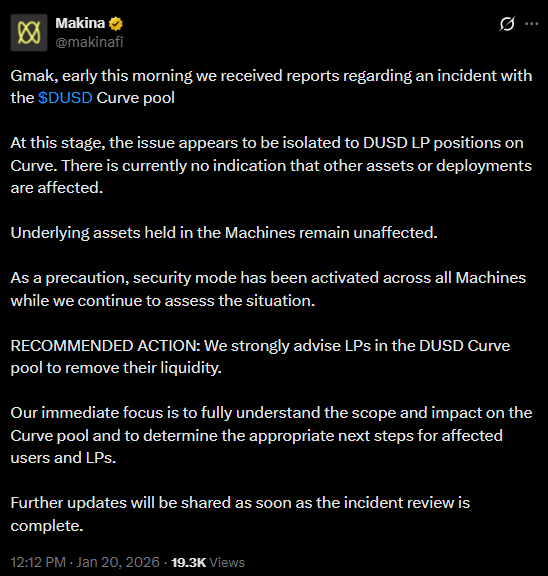
It said:
Interestingly, the protocol also stated that it has activated security mode across all Machines. However, it is still investigating the incident and plans to communicate the next steps for those affected.
The incident highlights the several vulnerabilities that DeFi protocols continue to face despite the advancements. This year, over three DeFi platforms have lost funds. Trubit fell to exploited vulnerabilities. YO Protocol suffered losses from human errors.